6 min read


Secure file sharing plays a critical role in helping organizations exchange sensitive information. Yet maintaining that security requires constant vigilance, as vulnerabilities can emerge even in widely adopted business software. In early 2023, IBM Aspera Faspex, a high-speed file-exchange application used to move large data sets, was found to contain a vulnerability that malicious hackers were actively exploiting. A 2014 Emmy winner for enabling faster media production workflows, Aspera has been adopted by organisations active in genomics and biomedical research, entertainment, military signals intelligence and financial services. It is hardly surprising that the US Cybersecurity and Infrastructure Security Agency labelled the vulnerability a significant risk.
But even when the technology behind secure online file sharing does not fail, the human factor still can. According to Verizon’s 2026 Data Breach Investigations Report, 62% of data breaches involved a human element, whether through error, social engineering, credential compromise or misuse. “People continue to play a very large role in incidents and breaches alike,” reads Verizon’s verdict.
So how can businesses make sure that the content employees share does not end up in the wrong hands? In this article, we look at what secure sharing is and which tools and practices can keep people productive while protecting sensitive data.
What is secure file sharing?
Secure sharing is the controlled exchange of files between authorized users. It combines encryption, identity verification and access permissions to prevent unauthorized viewing, alteration or disclosure, both while a file is being transferred and after it has been shared.
Secure file sharing can take place within or outside a local network, over a standard internet connection or through a private network connection such as a virtual private network. File-sharing solutions enable secure transfer by allowing users to restrict access and grant only authorized people permission to open, view, edit or download files.
In practice, secure sharing also requires control after a file has been sent. For example, a project owner may need to revoke a contractor’s access when an engagement ends, prevent downloads of a confidential document or review an activity log to see who opened a file.
What counts as a secure way to transfer files?
Broadly speaking, a secure file-transfer method preserves the confidentiality, integrity and availability of the data being shared. This is commonly referred to as the CIA triad:
-
Confidentiality means that only authorized people can access the file.
-
Integrity means that unauthorized changes can be detected or prevented.
-
Availability means that authorized users can access the file when they need it.
According to TechTarget, access control is also a key part of secure online file sharing. This might involve password-protected links, download restrictions, or, for stronger control and greater transparency, integration with the company’s identity and access management system.
Encrypted file sharing: a must-have tool for protecting documents online
When data is being shared, it can be intercepted, sent to the wrong person, overshared or exposed through a compromised system. For organisations moving sensitive information across networks and between users, this can lead to financial and reputational damage, operational disruption and regulatory consequences. Encrypted file-sharing can help reduce this exposure.
Encryption protects information by turning it into a coded form that cannot be read without the right key. With end-to-end encryption, files are encrypted before they leave the sender’s device and can only be decrypted by authorised recipients. This means the service provider and other intermediaries cannot read the files while they are being transferred or stored.
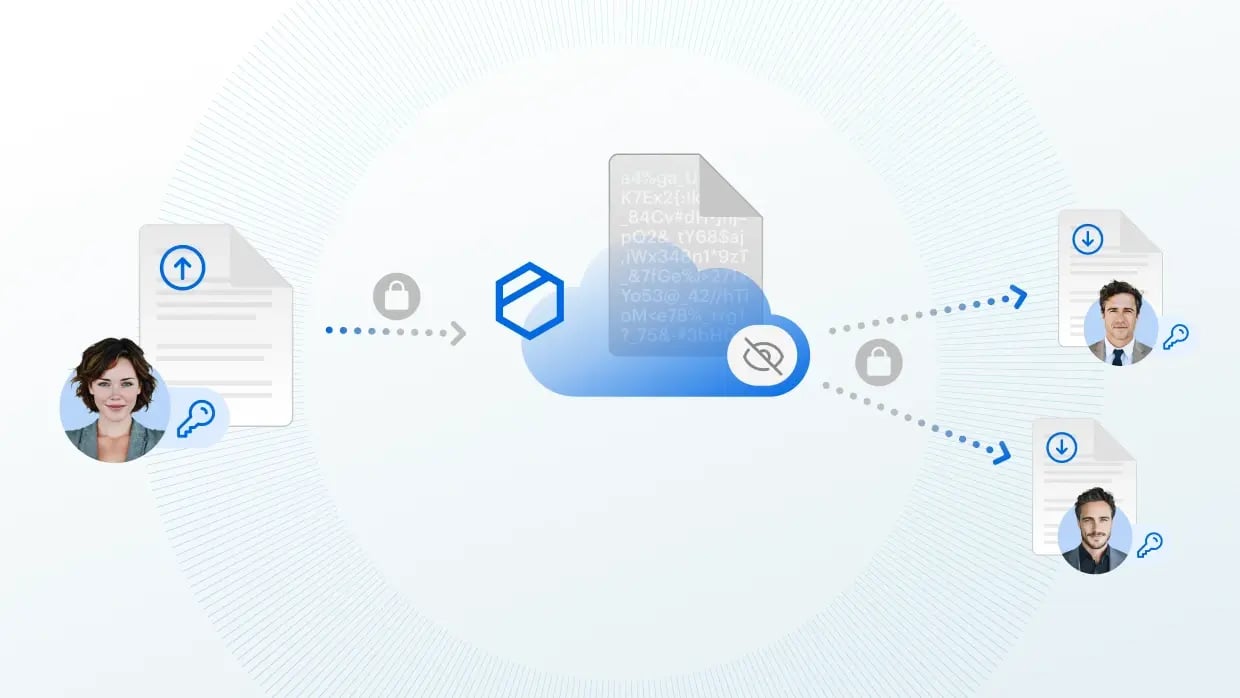
Encryption is only one part of secure file sharing. Organisations also need strong identity and access controls, secure devices and the ability to manage and revoke permissions.
A zero-knowledge architecture also provides an additional layer by ensuring that the provider does not have the information needed to decrypt customers’ files, reducing exposure even if the provider’s infrastructure is compromised.
Secure file sharing with clients: what not to do
According to a survey, more than half of US employees surveyed, 56%, used personal file-sharing services such as OneDrive, Google Drive, WhatsApp or Dropbox to share work-related files to save time and hassle, whether or not they were allowed to do so. One-third were fully aware that company policy prohibited business file sharing using personal tools and were familiar with the cybersecurity risks involved.
When an employee uploads a client contract to a personal cloud account, administrators may be unable to enforce retention rules, revoke access, preserve an audit trail or remove the file when the employee leaves. It is difficult to blame employees if approved tools make everyday sharing unnecessarily complicated. The harder it is for employees to access and share content, the more likely they are to look for workarounds that bypass security protocols and put company data and resources at risk.
Shadow IT is often a workflow warning, not simply an employee-awareness problem. If an approved sharing process requires too many logins, cannot accommodate external recipients or works poorly on mobile devices, employees are more likely to move files through personal email, messaging apps or unmanaged cloud accounts.
Whatever enterprise file-sharing solution you choose, ease of use should therefore be a priority. Security controls are effective only when employees can apply them in their everyday workflows.
How to send files securely: five ways to get file sharing right
1. Use end-to-end encryption to protect file content
As we’ve established, end-to-end encryption provides the highest level of data protection for users because it ensures that information gets encrypted before it leaves the sender’s device and remains encrypted until it reaches the intended recipient. Meaning that no third party has a chance to access the exchanged information.
End-to-end encryption is now widely used in the corporate world but in reality, many solutions only provide partial encryption or poor key management. Or in the worst case scenario, both.
Opt for a service that offers zero-knowledge, end-to-end encryption, making it impossible even for the service provider to access your encryption key and look into the contents of your files.
2. Choose a solution that works with your existing applications
This reiterates what we’ve said about usability: secure file-sharing solutions are only as secure as the workflows people actually follow. If they introduce friction or are difficult to use across devices and locations, employees may resort to tools that are familiar and convenient first and safe second, if at all.
Look for integration with the applications employees already use for daily work, such as email, productivity suites, identity platforms and mobile devices. A user who can replace an email attachment with an encrypted link from within Outlook is less likely to upload the same document to a personal account.
The same principle applies to external collaboration. Clients and partners should be able to access protected files without installing unnecessary software or creating multiple accounts, while the sender retains control over authentication, expiry dates, downloads and permissions.
3. Strengthen password security with multifactor authentication
MFA-enabled online services ask for a combination of two or more factors for identity verification. These include something you know, such as a password or PIN; something you have, such as a registered phone or security key; or something you are, such as a fingerprint or facial characteristic.
Multifactor authentication can dramatically reduce the risk of compromised passwords and account takeovers because an attacker who obtains one factor must still overcome another. Microsoft previously reported that MFA could block more than 99.9% of account-compromise attacks, according to this report.
4. Make sending documents securely via email practical
In and of itself, email isn’t exactly the most secure channel to share files over. Attachments create separate copies that can be forwarded, downloaded to unmanaged devices and retained after access should have ended. Traditional email also gives the sender limited control once a message has been delivered.
With the right secure file-sharing service, employees can continue working from their email client while replacing conventional attachments with encrypted links. Users of Tresorit’s add-in for Microsoft Outlook, for example, can encrypt emails in just one click, from subject lines to attachments, without key exchange, additional software integration, or new workflows on either side of the transmission.
5. Turn employees into your first line of defense
According to an OpenText study, 44% of employees surveyed relied on personal file-sharing solutions for work-related tasks because they were not aware that doing so was against company policy.
Organize regular, role-specific training to make sure staff are up to date on security protocols and understand how to use them. Training should include how to send encrypted files, how to check recipient permissions, when to set a link expiry date and what to do after accidentally sharing a document with the wrong person.
Is Tresorit the right secure file-sharing solution for your organization?
Tresorit may be a strong fit if you:
- Share confidential files externally: Teams can exchange contracts, financial records, personal data and intellectual property while controlling who can access each file, restricting downloads and revoking access when it is no longer needed.
- Need the cloud provider to remain unable to read your file content: Files are protected with zero-knowledge end-to-end encryption, meaning Tresorit does not possess the decryption information required to access their contents.
- Require granular access controls and consistent security policies: Administrators can manage permissions and apply measures such as two-step verification and sharing restrictions across teams.
- Want secure sharing to work within familiar workflows: Integrations with Gmail and Outlook allow employees to replace conventional attachments with protected sharing links while continuing to work in their existing email environment.
Tresorit may not be the most natural fit if your main priority is:
- An all-in-one productivity suite: Organizations seeking email, office applications, video conferencing, chat, storage and collaboration from a single provider may be better served by a broad workplace platform.
- Browser-based real-time co-editing: Teams whose main workflow involves several users simultaneously editing the same document may prioritize native co-authoring over controlled file sharing.
- Frequent transfer of very large files: Workflows centered on regularly delivering files larger than 5 GB, such as raw video or production archives, may require a purpose-built large-file transfer service.
Explore secure file sharing with Tresorit
This article was written in 2023 and updated in 2026.